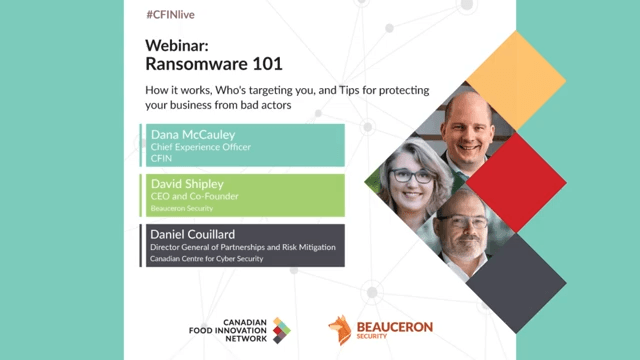
Here are the top four takeaways from the event:
1. Ransomware is big business.
Many ransomware operations are part of a sophisticated, multilevel criminal organization. There are now ransomware as a service providers who build and maintain the cloud criminal infrastructure and marketing of this malware. Sometimes these cybercriminals have the tacit approval of their nation states, and sometimes they are backed by nation states.
2. Food and beverage companies of all sizes can be targeted by ransomware.
Any organization that depends on their technology to run or scale is potentially susceptible and vulnerable to the impact of extortion via ransomware. The disruption caused by ransomware can affect companies in all areas, including production runs, inventory and ordering, invoicing customers, and scheduling staff.
3. Cybersecurity is as much about people as it is about technology.
Education and awareness of cybersecurity should be part of your company culture. Ransomware targets employees first by attempting to get them to click on phishing emails, links or attachments which can introduce malware to your company system. Once you establish a training and education program for employees technology such as multi-factor identification (especially with number matching), firewalls and anti-virus software can also be used to combat cybercrime.
4. All companies must have and practice a ransomware strategy.
Business owners and operators need to understand what their critical data is that they need to run their business, as well as how much risk they’re willing to accept. With this in mind they can build an incidence response team that includes experts from different areas of the company. A tabletop exercise on ransomware scenarios should be done at least once a year to plan and practice your response. The faster you are able to respond to ransomware, the less impact it will have on your business. The Canadian Centre for Cyber Security offers a Ransomware Playbook to help businesses plan a ransomware strategy.